As reported on November 7, 2026, Gnosis Pay disclosed unauthorized access to a legacy system that powers its branded debit cards. The company detected the access on November 3 and said certain customer information was exposed. It said it contained the incident within two hours, replaced compromised security credentials and addressed the vulnerability. According to Gnosis Pay, customer funds were not affected, and the separate enterprise platform that powers white-label card programs was untouched.
What changes for card payments: Gnosis Pay has made 3D Secure verification mandatory for online payments made with its cards until the affected system is retired on December 20. That adds a verification requirement to online card purchases; the reported breach does not mean card balances were accessed.
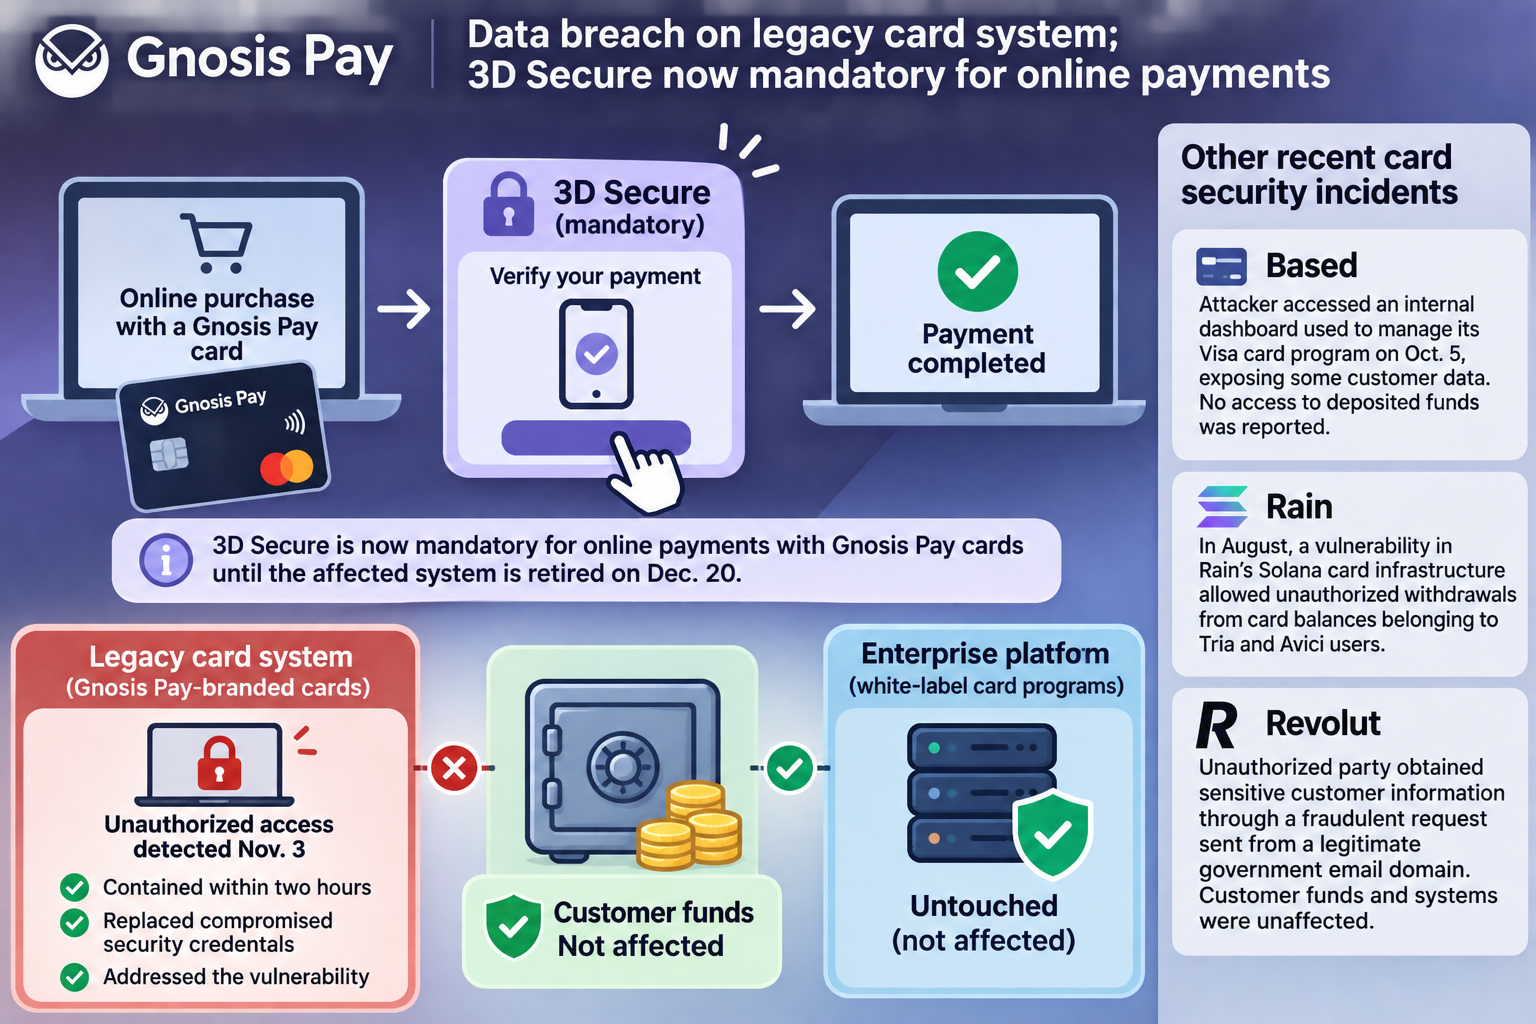
The distinction matters across card programs. Based said an attacker accessed a dashboard used to manage its Visa card program on October 5, exposing some customer data, but reportedly failed to access deposited funds. In August, a vulnerability in Rain’s Solana card infrastructure allowed unauthorized withdrawals from card balances belonging to Tria and Avici users. Revolut also said an unauthorized party obtained sensitive customer information through a fraudulent request sent from a legitimate government email domain; it said customer funds and systems were unaffected.