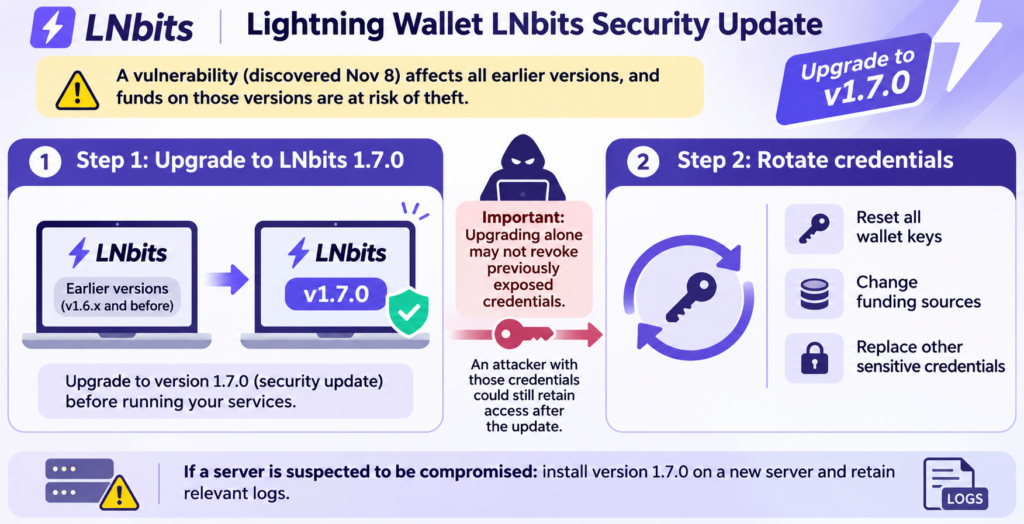
Originally reported November 11, 2026, at 09:31 (UTC+8). Citing an LNbits announcement, TechFlow reported that the Lightning wallet system had released version 1.7.0 as a security update and told all operators to upgrade before running their services.
LNbits said it discovered the vulnerability on November 8 and that all earlier versions were affected, putting funds on those versions at risk of theft. The project also warned that upgrading may not revoke credentials exposed beforehand: an attacker with those credentials could retain access after the update.
LNbits advised operators to reset all wallet keys, change funding sources and replace other sensitive credentials. If a server is suspected of being compromised, it recommended installing the new version on a new server and retaining relevant logs.
Source: techflowpost.com (originally published 2026-11-11 09:31 UTC+8)